RED HAWK // FIELD NOTES
What we're publishing,
testing & exploring.
Selected security research, technical breakdowns, investigations and practical security knowledge from Red Hawk.
Red Hawk solves real-world security problems through security validation, offensive and defensive consulting, research, and practical security engineering.
Web application, API, and network security assessments. Vulnerability assessment and configuration review.
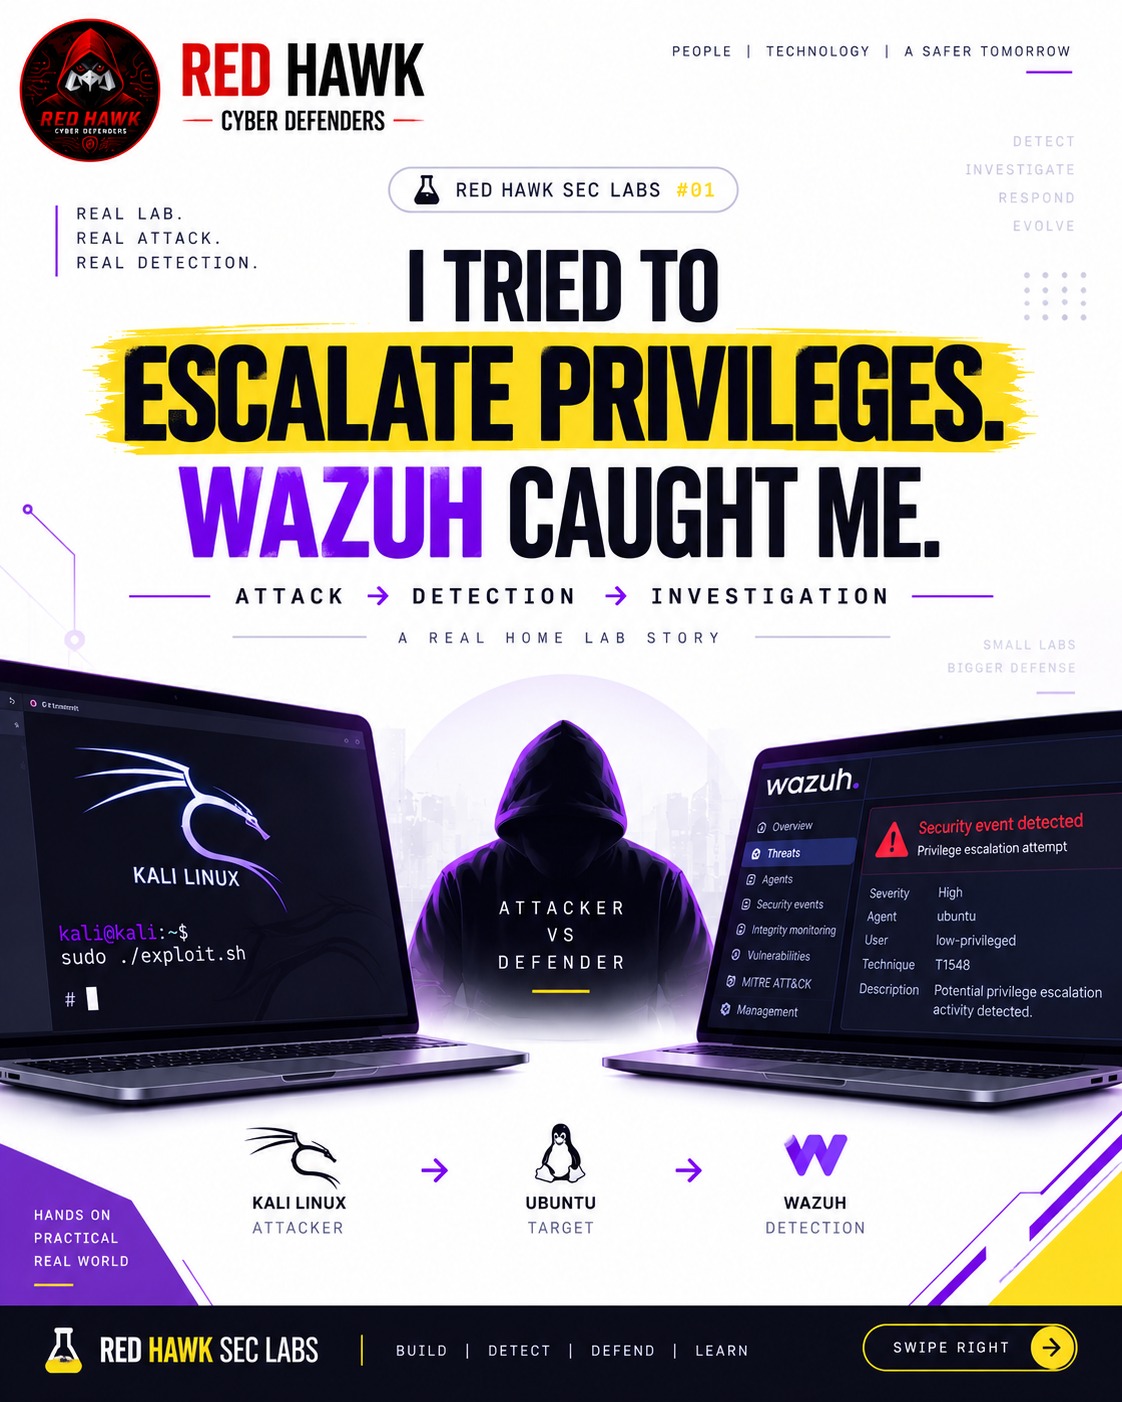
SIEM and EDR/XDR assessment, detection engineering, threat hunting, and SOC review.
Test whether your controls detect and respond as designed. Find → Attack → Observe → Detect → Respond → Fix → Retest.
SOAR playbooks, Python and n8n workflows, API integrations, and investigation automation.
OSINT, digital intelligence, entity research, and threat intelligence — primarily for government and law enforcement.
We keep the work focused, observable, and useful to the people who have to act on it.
Define the system, control, or assumption that needs evidence.
Run controlled attack scenarios against the agreed target.
Capture what your tools, teams, and workflows actually see.
Prioritize practical fixes by impact, effort, and operational risk.
Confirm the change and leave you with evidence you can use.
Security controls are often configured, but not confirmed. Red Hawk's validation methodology tests EDR, SIEM detection rules, SOC workflows, and response processes against real attack scenarios — so you know what works and what needs attention.
Start Validation →Red Hawk supports government and law enforcement with cybersecurity services and digital intelligence capabilities. Client identities remain confidential.
Discuss Requirements →Sec Labs is Red Hawk's internal research and development environment. We investigate real-world security problems, test assumptions, and document what we find — not what we assume.
We publish evidence-based security research focused on validation, detection, automation, and the failures that silently leave teams exposed.
A practical analysis of detection coverage, telemetry dependencies, fidelity, context, and operational usefulness.
Read research briefA structured analysis of direct and indirect prompt injection, retrieval pipelines, tool access, data exposure, and business impact.
Read research briefAn operational analysis of what security workflows are suitable for automation, where human judgment belongs, and how to validate automated outcomes.
Read research briefSelected security research, technical breakdowns, investigations and practical security knowledge from Red Hawk.
Tell us what you're trying to secure, test, investigate, or automate.